Do I need a compliance gap analysis?
 Leo HallowayApril 22, 2026
TL;DR
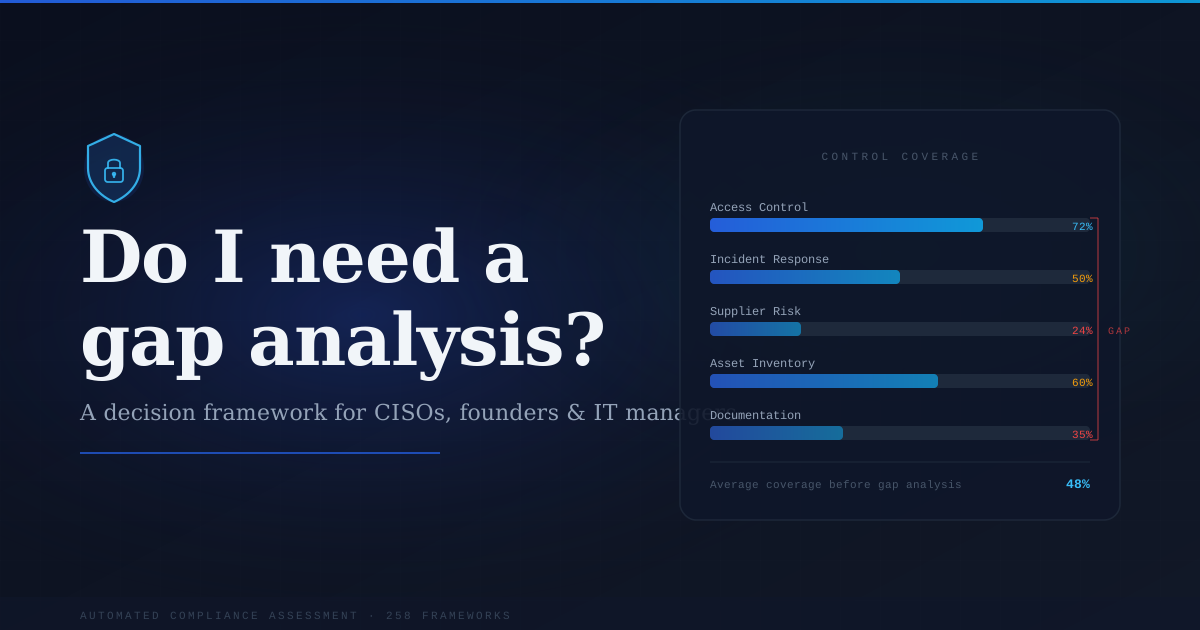
Most companies that skip a gap analysis do not know what they are skipping — they assume their existing controls map to a framework, and that assumption is wrong more than 60% of the time based on Vulnox assessment data, 2025.
The trigger is almost never regulatory. It is a customer audit, a cyber insurance renewal, or a sales deal that stalls on a security questionnaire.
Small companies in unregulated industries get hit hardest when they skip this step — not because regulators come after them, but because enterprise buyers do.
The most expensive gap to fix is never the technical one. It is the undocumented process that everyone follows but no one has written down.
A gap analysis does not tell you that you are compliant. It tells you exactly how far away you are, which is the only starting point that produces a realistic remediation plan.
The audit that nobody saw coming
A 35-person SaaS company in the Netherlands — B2B, selling HR workflow software to mid-market clients — had been operating for four years without a formal security framework. Their engineering team was good. They had SSO, enforced MFA, ran regular dependency updates, and used a reputable cloud provider. By most internal measures, they felt secure. Then a new enterprise client, a logistics company with 3,000 employees, sent over a vendor security questionnaire as part of procurement. Sixty-two questions. The SaaS founder answered honestly and returned it within two days. The deal went quiet. Three weeks later, the procurement contact called back and said their security team had flagged seven critical gaps — no formal incident response plan, no documented data retention policy, no evidence of access control reviews, and no mapping to any recognized framework. The deal did not fall through, but it was delayed by four months while the company scrambled to produce documentation. That four-month delay cost them the first-year contract value in delayed revenue, plus roughly 80 hours of the CTO's time building documentation from scratch under pressure.
The founder told us afterward: 'We thought secure meant safe. We did not know secure and documented were two different things.' That sentence captures exactly why the question of whether you need a compliance gap analysis is harder to answer than it looks.
'We thought we were fine' — and what that actually means
'We already have security controls in place. We use a good cloud provider, we have MFA everywhere, and our engineers follow best practices. Why would we pay for someone to tell us something we already know?'
Root cause:The assumption underneath this is that having controls in place is the same as having controls that are documented, tested, assigned to an owner, and mapped to a specific framework requirement. These are not the same thing. A cloud provider handles infrastructure security, not your application-layer access controls, your vendor management process, or your data classification policy. MFA is one control out of roughly 93 in ISO 27001 Annex A. Best practices followed informally by engineers are not the same as policies that can be evidenced to an auditor. What this complaint really reveals is a gap between technical hygiene and compliance readiness — two things that overlap but are not identical.
'We are not in a regulated industry. GDPR applies to us but we have a privacy policy and we do not sell data, so we are covered.'
Root cause:GDPR compliance is not a binary. Having a privacy policy satisfies one obligation. But GDPR Article 32 requires appropriate technical and organizational measures — and 'appropriate' is defined relative to the risk, not relative to what you have currently documented. What most companies in this position are missing is not malicious intent, it is evidence. If a data subject exercise request comes in, can you demonstrate a documented process for handling it within 30 days? If a breach occurs, do you have a 72-hour notification procedure written down and tested? The gap is usually not in what the company does — it is in what the company can prove.
'We had a penetration test done last year so we know our security posture is solid.'
Root cause:A penetration test tells you whether a skilled attacker can get into your systems. A compliance gap analysis tells you whether your policies, processes, and controls meet the requirements of a specific framework. These answer completely different questions. A company can pass a pentest and still have no asset inventory, no change management process, and no supplier security assessment procedure — all of which are required under ISO 27001 and similar frameworks. The pentest finding gives false comfort in the compliance context because it is scoped to technical exploitation, not organizational control coverage.
What a gap analysis actually does — and what it does not
A compliance gap analysis maps your current state against the requirements of a chosen framework and produces a structured list of what is missing, what is partially in place, and what is fully satisfied. That sounds straightforward. The complexity is in the word 'current state.' Determining current state requires collecting evidence — policies, screenshots, configurations, process documentation, interview outputs — and evaluating whether that evidence would satisfy an auditor. Most companies have some controls that are operational but undocumented, some that are documented but not followed, and some that simply do not exist. The gap analysis separates these three categories. That separation is what makes it useful. A list that says 'you are missing 23 controls' is not the same as a list that says 'you have 8 controls that exist in practice but need documentation, 7 that need to be built, and 8 that are partially implemented and need to be extended.' The first list produces anxiety. The second list produces a project plan.
Example
In ISO 27001, Annex A contains 93 controls across four themes. In Vulnox gap analysis assessments, the median company arrives with roughly 40 to 50 of those controls in some form of operational practice. But of those, only 20 to 30 are documented well enough to satisfy an auditor. The remaining 10 to 20 exist as tribal knowledge — things the team does without a written procedure. Those undocumented operational controls are the most expensive to fix not because they require technical work, but because they require time from people who are busy doing the work they have not yet documented.
Framework mapping is not universal. A control that satisfies ISO 27001 A.8.2 (Information classification) does not automatically satisfy NIST CSF PR.DS-1 or PCI DSS Requirement 3. If you are pursuing multiple frameworks simultaneously or planning to in the next 18 months, the gap analysis needs to be structured around your full target framework set, not just the most pressing one. This is an area where automated tools that support multi-framework mapping have a meaningful advantage over spreadsheet-based assessments.
What we find when companies think they are covered
Assessment base: Vulnox gap analysis assessment data, 2025, across SMB and mid-market clients primarily in EU and UK jurisdictions
The access control review gap
In 71% of SMB gap analysis assessments run through Vulnox in 2025, the company had no documented process for reviewing user access rights on a periodic basis. Most had deprovisioning processes triggered by offboarding, but periodic review — required under ISO 27001 A.8.5 and SOC 2 CC6.2 — was missing entirely. The finding surprised most clients because they conflated offboarding controls with access review controls.
This is consistently flagged during enterprise vendor audits. A buyer's security team will ask for evidence of the last access review cycle. If there is no documented process and no evidence of it running, that is an immediate finding — regardless of how technically secure the access control implementation is.
The supplier assessment blind spot
Across Vulnox assessments of companies using 10 or more SaaS tools, 84% had no formal supplier security assessment process. They had vendor contracts, sometimes data processing agreements, but no documented process for evaluating the security posture of their technology vendors before or after onboarding. ISO 27001 A.5.19 through A.5.22 cover this area explicitly.
If one of those unvetted SaaS tools experiences a breach that exposes your customer data, 'we had a DPA in place' is not sufficient to demonstrate due diligence. The gap analysis finding here is not just about compliance — it is about actual supply chain risk that the company was carrying without knowing it.
The incident response plan that exists but has never been tested
About 55% of companies that arrive at a gap analysis with an existing incident response plan have never run a tabletop exercise or tested the plan in any documented way. The plan exists. It has never been challenged. Under most frameworks, a plan that has never been tested is treated almost identically to a plan that does not exist — because the evidence requirement is not just documentation, it is evidence of operationalization.
This is the finding that lands hardest because clients feel they have done the work. They wrote the plan. The issue is that writing a plan and having a functioning incident response capability are different things, and auditors — including customer security teams — know how to probe that distinction.
Undocumented asset inventories in cloud-native environments
For companies running entirely in cloud environments, 68% had no asset inventory that covered ephemeral resources — containers, serverless functions, short-lived virtual machines. Their asset inventory covered servers and endpoints but was blind to dynamic infrastructure. This is a specific failure mode of cloud-native environments that older inventory frameworks were not designed to catch.
Under NIST CSF and ISO 27001, asset management starts with knowing what you have. If your inventory is incomplete, every downstream control — vulnerability management, patch management, access control — is built on an incomplete foundation. The gap analysis surfaces this before an auditor does.
The companies that need this most are the ones who think they are exempt
Common belief
Compliance gap analysis is for regulated industries — financial services, healthcare, companies handling payment data. If you are a SaaS company, a professional services firm, or a tech startup that does not touch regulated data categories, you do not need one.
What we found
The industries most represented in Vulnox gap analysis assessments are not financial services or healthcare. They are B2B SaaS, professional services, and managed service providers — sectors with no direct regulatory framework mandate but with significant enterprise customer exposure. Vulnox assessment data, 2025.
This assumption gets tested the moment you try to sell to an enterprise customer, renew your cyber insurance, or respond to a data subject access request under GDPR. Enterprise procurement teams now routinely conduct vendor security assessments as part of onboarding. The threshold has dropped significantly — buyers with 500 or more employees are applying security questionnaire requirements to vendors of all sizes, including early-stage startups. The compliance requirement is not coming from a regulator. It is coming from your customers. And unlike a regulator, a customer does not give you a remediation period. They just do not sign the contract. We found that 43% of SMB clients who came to Vulnox for a gap analysis were driven there by a specific lost or stalled sales deal, not by a regulatory deadline. That number was under 20% three years ago. The shift is structural: enterprise security teams are effectively outsourcing compliance enforcement to their vendor selection process.
A self-assessment you can run right now
- Step 1
Check whether you have a target framework
Output:A named framework or a shortlist of two. If you have genuinely no external driver, you still need to pick one as a baseline — ISO 27001 is the most broadly accepted starting point for EU-based companies.
Purpose:A gap analysis only makes sense relative to a specific framework. If you do not know which framework your customers, auditors, or insurers will hold you to, you cannot close gaps meaningfully. Start by identifying whether any of your current or target customers have referenced ISO 27001, SOC 2, NIST CSF, or a specific questionnaire format in their vendor assessment process.
- Step 2
List the evidence you could produce today if asked
Output:A rough three-column list. The 'not documentable' column is your immediate gap list.
Purpose:Do not assess what controls you have. Assess what you could prove. Write down the 10 most likely questions an auditor or enterprise buyer would ask — incident response plan, access review evidence, data classification policy, supplier assessment records, backup test results — and mark each one as documentable now, documentable with work, or not documentable. This exercise alone surfaces the most critical gaps without any tool.
- Step 3
Identify your trigger timeline
Output:A date or date range. If there is no external trigger, set a self-imposed one. Companies with no deadline almost never complete the remediation work.
Purpose:Is there a specific event driving this — a customer audit, a certification deadline, an insurance renewal, a new market you are entering? The timeline determines whether you have the runway to do this properly or whether you need to triage. A gap analysis completed three weeks before a customer audit is still valuable but produces a different kind of output than one completed six months before a certification target.
- Step 4
Estimate your current documentation coverage
Output:A count out of eight. If you have fewer than four, you are at the beginning of this journey and a gap analysis will generate a long list of fundamentals. If you have six or more but they have not been reviewed in over 12 months, the gap is likely in evidence of operationalization, not in documentation existence.
Purpose:Go through your policy folder — wherever it lives — and count how many of the following you have in a written, dated, owner-assigned document: information security policy, acceptable use policy, access control policy, incident response plan, business continuity plan, data classification policy, change management procedure, supplier management policy. Eight is the minimum viable set for most frameworks.
- Step 5
Ask whether the cost of not knowing is higher than the cost of finding out
Output:A rough comparison. If the expected cost of a compliance failure in the next 12 months is higher than the cost of the analysis, the decision is straightforward.
Purpose:The analysis costs money and time. The question is whether the alternative — operating without a structured view of your compliance posture — carries a higher expected cost. Consider: the value of your next enterprise sales opportunity, your cyber insurance deductible, the cost of a 72-hour breach response with no documented procedure, and the reputational cost of failing a customer security audit. These are not hypothetical. They are the actual cost structure that makes the investment calculation real.
Where this is going — and what to expect
By 2027, cyber insurance underwriters will require documented gap analysis evidence as a condition of coverage for SMBs above a revenue threshold, not just as a pricing factor
Insurers are already using security questionnaire outputs to price policies. The next step is requiring evidence of structured control assessment — not self-reported questionnaire answers, but auditable documentation produced by a third-party or automated process. The loss ratios in SMB cyber insurance have been deteriorating since 2022. Underwriters are moving from pricing risk to declining unassessable risk. A company that cannot demonstrate a structured control review will become uninsurable before it becomes non-compliant in the regulatory sense.
Confidence: highWatch for changes in cyber insurance application forms between 2025 and 2027. If more than three major underwriters add a mandatory gap analysis evidence field — not a question about whether you have one, but a field requiring upload of documentation — the prediction is confirmed.A new failure mode will emerge in the next 18 months that we do not yet have a name for: compliance documentation that is AI-generated, policy-complete, and operationally empty
Generative AI makes it trivially easy to produce a full policy library — incident response plan, acceptable use policy, data classification policy — in under an hour. These documents will be syntactically correct and framework-mapped. They will also describe processes that do not exist, assign ownership to roles that are not filled, and reference tools that are not in use. The result will be a company that passes an initial document review but fails any operational audit or tabletop exercise. We are already seeing early evidence of this in client assessments where submitted policies reference procedures that the team has never heard of.
Confidence: highIf auditors and enterprise security teams begin adding a 'policy operationalization' question to vendor assessments — asking not just for the document but for evidence that the process described in it was actually followed — within 18 months, the prediction is confirmed.
My honest take on when you should skip it
This is my opinion, clearly labeled as such. There are situations where a formal gap analysis is genuinely the wrong first step. If you are a five-person company with no enterprise customers, no regulated data, and no immediate certification target, the most valuable thing you can do is build the four or five foundational policies that every company should have — information security policy, incident response plan, access control policy, data protection policy — and start following them. A gap analysis on a company with no policy foundation produces a 40-item remediation list that overwhelms a small team and often results in nothing getting done. Fix the foundation first. Get the gap analysis when you have something to measure against a framework. The tool is most powerful when it tells you the distance between where you are and where you need to be — and that distance is measurable only when 'where you are' has some structure to it.
Counterargument
The strongest counterargument is that waiting until you have a policy foundation before running a gap analysis is exactly the kind of delay that leaves companies exposed. A gap analysis on a bare foundation still tells you the priority order of what to build — and priority order matters. Without it, companies tend to build the policies they find easiest to write, not the ones that close their most critical risks first. There is a reasonable case that even a company with minimal documentation should run the analysis before building, not after. I do not dismiss that argument.
So do you need one?
Ask yourself the five questions in the self-assessment above and be honest about the answers. If you have an enterprise customer in your pipeline, a cyber insurance renewal in the next six months, or a certification target in the next year, the answer is yes — and the right time to start is before the external pressure arrives, not in response to it. If none of those apply and your policy foundation is genuinely underdeveloped, build the foundation first and schedule the gap analysis for 90 days out. The mistake that costs companies the most is not running the analysis wrong. It is running it at the wrong moment in their readiness cycle, getting a list they cannot action, and treating the resulting paralysis as evidence that the exercise was not useful. Run it when you can use the output. But if you are asking this question, there is a reasonable chance that moment is now.
Further Reading
compliance framework automation
How We Mapped 258 Compliance Frameworks to a Single Automated Audit SystemSPARTA Compliance Guide
SPARTA Compliance Guide: Control Gap Analysis FrameworkPDPA Compliance Guide
PDPA Compliance Guide: Security Control Gaps for MalaysiaVulnox Service
compliance gap analysisISACA
ISACA information security governanceNIST Cybersecurity Framework
NIST Cybersecurity FrameworkISO 27001
ISO 27001 information security standard
Frequently Asked Questions
Do I need a compliance gap analysis if I am not in a regulated industry?
Possibly yes. In Vulnox assessment data from 2025, 43% of SMB clients who requested a gap analysis were driven by a stalled or lost enterprise sales deal, not a regulatory requirement. Enterprise buyers now routinely apply security questionnaire requirements to all vendors regardless of size or industry.
What is the difference between a penetration test and a compliance gap analysis?
A penetration test tells you whether a skilled attacker can compromise your systems. A gap analysis tells you whether your policies, processes, and controls meet a specific framework's requirements. A company can pass a penetration test and still fail a compliance audit for missing documentation, process gaps, or unreviewed access controls.
How long does it take to complete a compliance gap analysis?
An automated gap analysis like Vulnox delivers structured findings within hours of evidence submission. Manual or consultancy-led assessments typically take two to six weeks depending on company size and framework scope. The remediation work that follows the analysis is typically three to nine months for an SMB targeting ISO 27001.
What frameworks does a gap analysis cover?
It depends on the tool or provider. Vulnox supports 258 frameworks including ISO 27001, SOC 2, GDPR, HIPAA, PCI DSS, NIST CSF, and others. Most companies need to prioritize one or two frameworks based on their customer base and geographic market before running the analysis.
What is the most common gap finding in SMB assessments?
Based on Vulnox assessment data from 2025, the most common finding is the absence of a documented access control review process. 71% of SMB assessments flagged no periodic access review procedure, despite most companies having offboarding controls in place. The second most common is missing supplier security assessment documentation.
Can I do a compliance gap analysis myself without a tool?
Yes, partially. The self-assessment workflow in this article gives you a starting point. The limitation of a manual self-assessment is that it relies on your own knowledge of what a given framework requires, which is typically incomplete. Automated tools map your evidence against specific control requirements across multiple frameworks simultaneously, which reduces the risk of overlooking less visible gaps.
What happens if I fail a customer security audit?
In most cases, a failed customer security audit does not immediately kill a deal — but it creates a remediation period during which the sale is stalled. Based on the scenario documented in this article, a four-month remediation delay cost a 35-person SaaS company roughly 80 hours of CTO time plus the first-year contract value in delayed revenue. Enterprise buyers with strict security requirements may decline to proceed entirely if critical gaps are not remediated within their procurement timeline.
Related Articles
GovRAMP Moderate authorization: why the Significant Change Request process catches providers off guard
GovRAMP Moderate is the first tier where you need a government sponsor, annual 3PAO reassessment, and a Significant Change Request process that can pause normal product releases for months. Most providers who stall post-authorization were not prepared for what maintaining Moderate status actually costs operationally.
GovRAMP Low+ authorization: the impact level that punishes providers who get the CUI boundary wrong
GovRAMP Low+ is where providers handling limited Controlled Unclassified Information land — or discover they should not be there. The defining failure is not a missing control. It is a CUI boundary that was drawn before anyone asked what data the government actually sends through the system.
GovRAMP High authorization: why FIPS-validated crypto and personnel security controls catch providers off guard
GovRAMP High is where cloud providers discover that having strong encryption is not the same as having FIPS 140-2 validated encryption — and that distinction alone has derailed authorizations from vendors who passed every other control family. The architectural constraints at High are qualitatively different from every lower tier.
Ready to Secure Your Digital Assets?
Get a comprehensive vulnerability assessment for your website today.