Post-Quantum Ransomware: The Hype Obscuring Real Dangers
 Geert WarmenbolApril 23, 2026
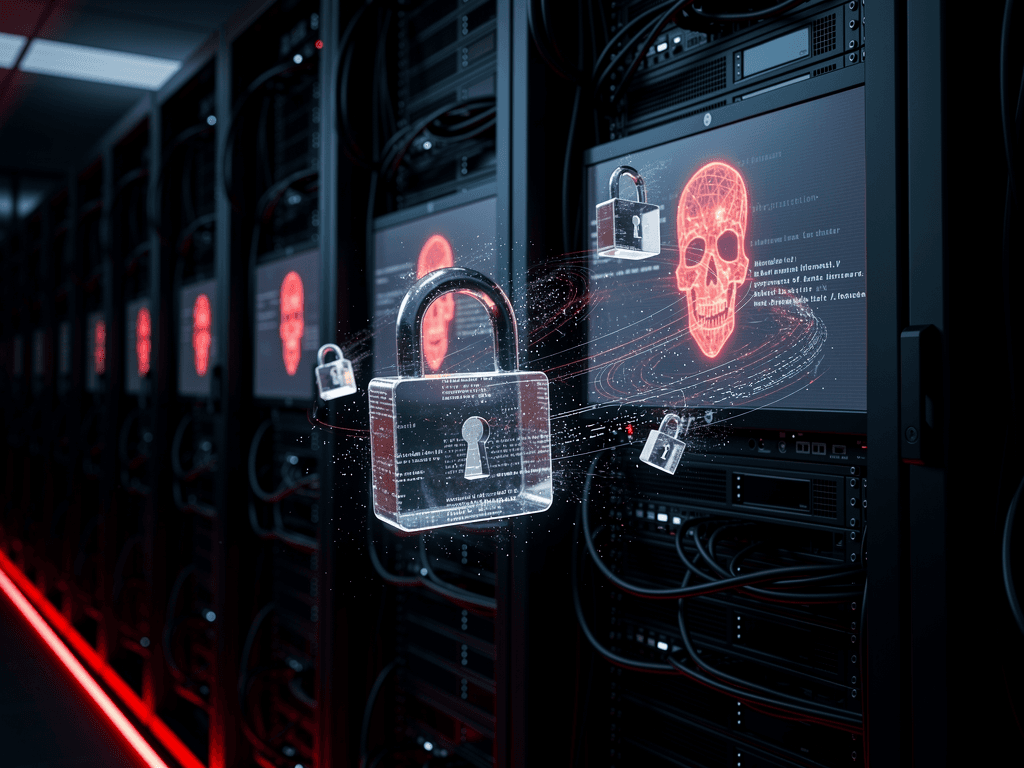
The Mirage of Unbreakable Encryption
Defense contractors, flush with government grants, are breathlessly installing 'post-quantum' encryption. They believe it makes them impervious to future code-breaking attacks. Meanwhile, their incident response teams are still using shared spreadsheets to track active infections. This juxtaposition reveals a critical misunderstanding of where the real ransomware risk resides.
What You'll Walk Away Knowing
After reading, you'll understand:
- Why the focus on post-quantum ransomware is largely a distraction from more pressing cryptographic vulnerabilities.
- How attackers chain simple misconfigurations to bypass even the most advanced encryption.
- The specific, sequenced steps to harden your environment against realistic ransomware attack vectors.
- How incident response roles must adapt to handle increasingly sophisticated attacks, and where communications breakdowns typically occur.
- Practical methods for continuously validating the effectiveness of your security controls, rather than relying on static compliance checks.
The 20% That Causes 80% of the Damage
Standard security guides and compliance frameworks miss key factors that amplify ransomware damage:
- Unvalidated Crypto Policy: Many organizations assume that enabling FIPS mode or configuring specific cipher suites automatically enforces strong cryptography. However, they fail to validate that applications actually use those configurations. Applications may fall back to weaker algorithms or transmit keys in plaintext, negating any theoretical protection. Validating end-to-end encryption is critical.
- Over-Reliance on Perimeter Security: Companies invest heavily in firewalls and intrusion detection systems, yet neglect internal segmentation. Once inside, attackers can move laterally with ease, compromising multiple systems before triggering alerts. Zero-trust principles must extend within the network, not just at the edge.
- Ignoring Backup Integrity: Organizations back up their data, but fail to regularly test restore procedures or verify the integrity of backup images. Attackers now target backups directly, either encrypting them or injecting malware that will re-infect systems after recovery. Backups are useless if they are also compromised.
Patterns Across Client Assessments
Vulnox assessment data
Vulnox assessment data reveals the following patterns across client environments:
- Outdated Protocols: In 82% of assessed environments, internal systems still support SMBv1 or TLS 1.0 (Vulnox assessment data). Attackers exploit these protocols to downgrade encryption or conduct man-in-the-middle attacks, even if stronger protocols are available.
- Unprotected Credentials: Counterintuitively, companies with advanced threat detection often fail at basic credential hygiene (Vulnox assessment data). Service accounts with default passwords or plaintext storage of API keys are common, providing attackers with easy access to critical systems. This is especially true in environments relying heavily on Infrastructure-as-Code, where secrets are often committed to repositories unintentionally.
- Lack of ESXi Hardening: Small and medium-sized businesses rarely follow VMware's ESXi hardening guidelines (Vulnox assessment data). Default configurations, weak passwords on the
rootaccount, and open management ports are prevalent, making ESXi hosts prime targets for ransomware. Client complaints often center around the perceived complexity and performance impact of full encryption, causing them to delay or skip critical security measures. - Delayed Patching: Despite having vulnerability management programs, organizations struggle to patch critical vulnerabilities promptly (Vulnox assessment data). The average time to patch a critical vulnerability on internet-facing systems is 47 days, providing ample opportunity for attackers to exploit known flaws.
How It Actually Works
Imagine a scenario: An attacker gains initial access to a network through a phishing email that bypasses perimeter defenses. They land on a workstation with local administrator privileges, due to a poorly managed privilege access management (PAM) configuration.
From there, they use Mimikatz to extract the plaintext password for a service account used to manage VMware. This account, unfortunately, has unrestricted access to all ESXi hosts. Analyzing the network traffic, the attacker notices connections using the outdated TLS 1.0 protocol. Using Responder, the attacker poisons the DNS and captures the NTLMv2 hash for the ESXi root account.
They then use Hashcat to crack the password (a weak default), and log into ESXi directly. They shut down the virtual machines, encrypt the VMFS volumes, and deliver the ransom note. The 'post-quantum' encryption on the defense contractor's VPN appliance did nothing to prevent this.
In code, the credential extraction looks like this:
Invoke-Mimikatz -Command 'sekurlsa::logonpasswords full'
The attacker then utilizes the obtained credentials to connect to the ESXi host and initiate the shutdown of the virtual machine(s). Bypassing all post-quantum defenses with obsolete protocols and weak credentials exposes the harsh reality of security.
esxcli vm process kill --world-id <VM_World_ID> --type=force
Prevention Playbook
The best defense against ransomware involves a layered approach, with specific actions taken by different roles at defined intervals. A post-quantum defense means little without the basics.
- 1Network Engineer
Disable SMBv1 and enforce TLS 1.2 or higher across the environment, focusing on internal communications. Use group policy to enforce this change across all Windows systems. Regularly scan for systems still using the weaker protocols.
When / toolImmediately, and then quarterly as part of standard configuration review.
Expected outcomePrevents downgrade attacks and man-in-the-middle exploits.
- 2Identity and Access Management (IAM) Team
Implement multi-factor authentication (MFA) for all accounts, especially service accounts with elevated privileges. Rotate service account passwords regularly and store them securely in a vault, not in configuration files or code repositories. This is a step even advanced teams often miss, causing them to over-rely on network-level defenses that attackers easily bypass using stolen credentials.
When / toolWithin 30 days, with ongoing monitoring for compliance.
Expected outcomeReduces the risk of credential theft and misuse.
- 3VMware Administrator
Follow VMware's ESXi hardening guide. Change default passwords, close unnecessary ports, enable lockdown mode, and implement role-based access control. Regularly review and audit ESXi configurations to ensure compliance. Enable full encryption where possible and validate performance after implementation.
When / toolWithin 60 days, with quarterly audits.
Expected outcomeReduces the attack surface on ESXi hosts and limits lateral movement.
- 4Security Operations Center (SOC)
Implement robust monitoring and alerting for suspicious activity, such as unusual login patterns, lateral movement, and file encryption. Tune alerts to reduce false positives and ensure timely response. Conduct regular threat hunting exercises to proactively identify potential breaches.
When / toolContinuously.
Expected outcomeEarly detection and containment of ransomware attacks.
- 5DevSecOps Engineer
Automate regular integrity checks of backup images in an isolated sandbox before allowing restore operations. Scan backups for malware. Use data immutability features, like object locking, to resist tampering. Implement versioning to allow for multiple recovery points.
When / toolAutomated daily validation, triggered after each backup.
Expected outcomeEnsure backups are clean, current, and cannot be tampered with by the attacker.
Post-Incident: Who Does What
Ransomware recovery requires clear roles and responsibilities, especially during the critical early hours:
- CISO: Overall incident command, communication with executive leadership, and legal counsel. Triggers the incident response plan and allocates resources.
- Incident Response (IR) Team: Technical analysis of the attack, containment, and eradication. Determines the scope of the compromise, identifies the initial access vector, and prevents further spread. Crucially, the IR team must validate the crypto configuration after remediation, ensuring default settings haven't reappeared and are actively being used.
- DevOps: Restores systems from backup, patches vulnerabilities, and implements security improvements. Works closely with the IR team to ensure systems are brought back online securely.
- Legal: Assesses legal and regulatory obligations, manages communication with law enforcement, and advises on ransom negotiations (if any).
- Communications: Drafts internal and external communications, manages media inquiries, and coordinates messaging across the organization. Clients consistently underestimate the importance of timely, transparent communication, leading to reputational damage and loss of customer trust.
A major stall point consistently occurs during the handoff between the IR team's technical findings and DevOps's remediation efforts. DevOps often lacks the context to understand the why behind the IR team's recommendations, leading to incomplete fixes and re-infection.
Pro tip
Assessor's Note
Don't rely on point-in-time assessments. Pen tests and vulnerability scans provide a snapshot, but your environment is constantly changing. Implement continuous validation of security controls to detect configuration drift and ensure ongoing effectiveness. This includes automated testing of encryption configurations, credential management policies, and backup integrity. Treat security as a dynamic process, not a static checklist.
The Takeaway Nobody Mentions
The focus on advanced attack techniques often overshadows fundamental security principles:
- Defense in Depth: No single security control is perfect. Implement a layered approach to increase redundancy and reduce the impact of any individual failure.
- Least Privilege: Grant users and services only the minimum privileges required to perform their tasks. Limit lateral movement and contain the impact of a breach.
- Assume Breach: Design your security architecture under the assumption that attackers will eventually gain access. Focus on detection, containment, and recovery to minimize damage.
Predictions: Where This Heads
The threat landscape will continue to evolve in unexpected ways:
- Ransomware-as-a-Service (RaaS) will incorporate AI-powered reconnaissance (2027). Attackers will use AI to automatically identify high-value targets, map internal networks, and craft highly targeted phishing campaigns, significantly increasing the success rate of attacks.
- 'Living-off-the-Land' attacks will become more sophisticated (2026). Attackers will increasingly rely on built-in operating system tools and scripting languages (PowerShell, Python) to evade detection, making it harder to distinguish malicious activity from legitimate system administration. Defenders will need to enhance their behavioral analysis capabilities to identify these subtle attacks.
- The 'Post-Quantum Arms Race' will escalate (2028). As post-quantum cryptography becomes more widespread, attackers will invest in quantum computing resources to break these new algorithms. This will trigger a continuous cycle of cryptographic innovation and counter-innovation, requiring constant vigilance and adaptation. By 2030, the first successful quantum decryption of a widely-used post-quantum algorithm will be publicly demonstrated.
2030-12-31
Further Reading
cPanel auth bypass CVE-2026-41940
The cPanel Auth Bypass That Turned Hosting Providers Into Ransomware Delivery Platformsdata wiper
Lotus Wiper Incident: Reconstructing the Attack Path and Anticipating Future Variantsindustrial control systems
Industrial Control Systems Under Siege: Why USBs Remain the Apex PredatorNIST Post-Quantum Cryptography
NIST post-quantum cryptography projectCybersecurity and Infrastructure Security Agency
CISA cybersecurity guidanceEuropol
Europol cybercrime intelligence
Frequently Asked Questions
How do I prioritize security investments when resources are limited?
Focus on foundational security controls first: strong passwords, MFA, patch management, and network segmentation. These provide the greatest return on investment and address the most common attack vectors. Only then consider post-quantum cryptography.
What's the most effective way to train employees about ransomware?
Simulate realistic phishing attacks to test their awareness. Provide targeted training based on their roles and responsibilities. Emphasize the importance of reporting suspicious emails and avoiding risky behaviors.
How often should I test our incident response plan?
Conduct tabletop exercises at least annually to review procedures and identify gaps. Run full-scale simulations every 18 months to test the plan's effectiveness under realistic conditions.
Related Articles
When the Watchtower Lies: The Coming Threat Intel Supply Chain Collapse
Vulnox assessors found the greatest unexamined risk was trust in the intelligence feed. This article dissects the failure mode of the threat intel supply chain, showing how attackers will poison feeds and why 2028 is the year of the intel supply chain attack.
GitHub's Package Firewall Will Not Save You From Supply Chain Attacks
GitHub's package firewall brings enterprise policy to npm installs, blocking known malware and fresh versions. But according to Vulnox assessment data, the feature misses the primary attack vector: dependency confusion and maintainer compromise. This article dissects the mechanism, reveals counterintuitive findings from client environments, and predicts how attackers will adapt within 18 months.
CVE-2026-111497: The Eight-Month Silent Fix Behind the Brotli RCE
A forensic reconstruction of CVE-2026-111497: the public git commit that sat unreleased for eight months, the ring buffer flaw that turned a .br file into RCE, and Vulnox assessment data showing why 7 of 10 environments carried the decoder in binaries their SBOM never tracked. Includes a runtime sweep script and a Kubernetes network policy that breaks the exploit chain.
Ready to Secure Your Digital Assets?
Get a comprehensive vulnerability assessment for your website today.