ISO/SAE 21434 automotive cybersecurity: where compliance ends and risk begins
 Amara OkaforMay 5, 2026
Key takeaways
ISO/SAE 21434 requires a Cybersecurity Management System covering the full vehicle lifecycle — but in practice, most OEM implementations cover development and release and treat post-production monitoring as a documentation obligation rather than an operational one.
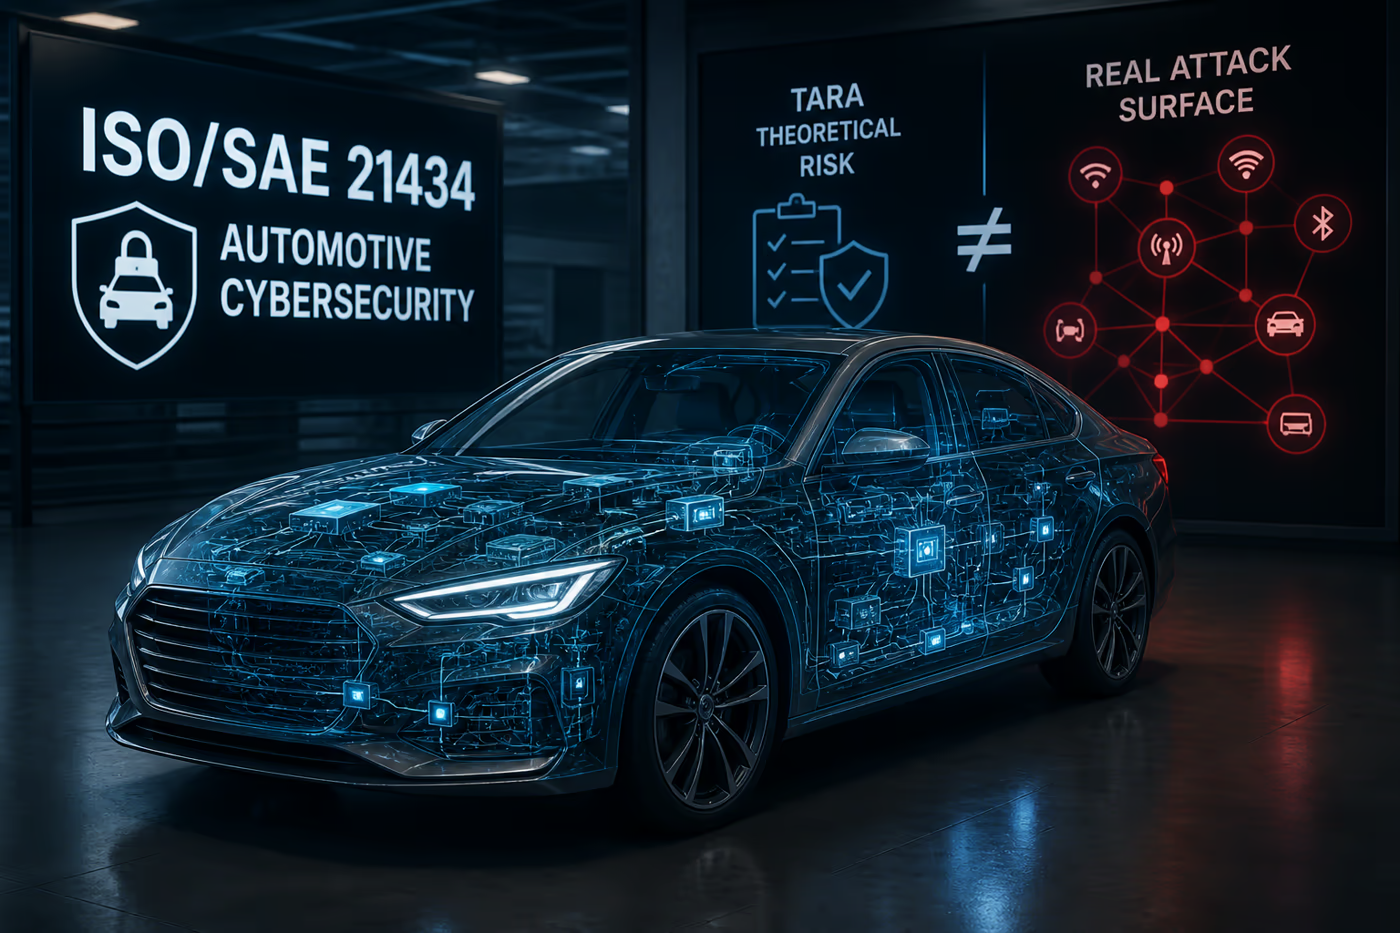
The standard''s Threat Analysis and Risk Assessment (TARA) methodology is its most time-intensive requirement and its most commonly misimplemented one — organizations produce TARA artifacts that are complete on paper but were never validated against what an attacker can reach from outside the vehicle.
UNECE WP.29 Regulation 155 made ISO/SAE 21434 operationally mandatory for type approval in the EU, Japan, and Korea for new vehicle types from July 2022 — compliance with R155 without genuine 21434 implementation is achievable on paper and leaves measurable attack surface unaddressed.
In Vulnox assessments of connected vehicle environments, the most consistent gap is at the Tier 1 and Tier 2 supplier boundary — OEM cybersecurity programs are reasonably mature; supplier CSMS implementations are frequently nominal.
The standard explicitly covers the full product lifecycle including end-of-life, but cybersecurity obligations for vehicles already in the field — particularly over-the-air update integrity and post-production vulnerability monitoring — are the least operationalized sections in assessed programs.
ISO/SAE 21434 does not prescribe specific technical controls, which gives implementers flexibility and gives auditors almost no basis for distinguishing a strong implementation from a weak one at the evidence level.
TL;DR
ISO/SAE 21434 is a serious standard that the automotive industry has largely turned into a documentation exercise. The TARA gets written. The supplier contracts get updated. The CSMS gets certified. The attack surface of the vehicle — what an adversary actually sees when they point a tool at a connected ECU or a telematics interface — is rarely mapped with the same rigor the standard demands on paper. The compliance program and the security program are running in parallel and not talking to each other.
The TARA that had never seen the car
A Tier 1 supplier of telematics control units had completed a full TARA for their flagship product. The documentation was substantial — damage scenarios mapped, threat scenarios catalogued, risk values assigned, cybersecurity goals defined. It had passed OEM review and was part of a type approval submission. When we were engaged to perform an independent technical assessment of the same unit, we started where attackers start: external interfaces. The cellular modem interface accepted connections on three ports that were not in the TARA''s attack path analysis. The diagnostic interface — accessible via a standard OBD-II connector — responded to unauthenticated session requests in a way that the TARA had assessed as mitigated by an access control requirement. The access control requirement existed in the design specification. It had not been implemented in the production firmware.
The TARA was not wrong. It had correctly identified the threat scenarios and specified the mitigations. What it had not done — and what ISO/SAE 21434 requires but cannot enforce — was verify that the mitigations were present in the actual product. The gap between the cybersecurity concept and the implemented system is where most automotive cybersecurity risk lives. The standard has rigorous process requirements for getting from concept to implementation. It has limited mechanisms for confirming the journey actually completed.
What ISO/SAE 21434 requires and where the architecture breaks
ISO/SAE 21434:2021 covers cybersecurity engineering for road vehicles across the full lifecycle: concept, development, production, operation, maintenance, and decommissioning. Its central requirement is a Cybersecurity Management System — an organizational framework that ensures cybersecurity activities are planned, executed, and maintained across all these phases. The CSMS is what UNECE R155 type approval auditors check. It is also the layer most disconnected from actual vehicle security.
The standard''s technical core is the Threat Analysis and Risk Assessment methodology. TARA requires organizations to identify damage scenarios (what harm could result from a cybersecurity attack), threat scenarios (how an attacker could cause that harm), and attack paths (the technical sequence an attacker would follow). Each threat scenario gets a risk value based on impact and attack feasibility. Cybersecurity goals are then derived from the risk values, and those goals drive the technical design.
The architecture breaks at three specific points. First, attack feasibility assessment in TARA is notoriously difficult to calibrate correctly. The standard provides a framework — elapsed time, specialist expertise, knowledge of the item, window of opportunity, equipment — but calibrating these factors requires genuine offensive security knowledge that most automotive engineering teams do not have internally. The result is attack feasibility systematically underestimated for novel attack paths and overestimated for well-documented ones. Risk values are wrong in predictable directions.
Second, the standard treats the supplier relationship as a contractual boundary. OEMs are required to ensure that their suppliers implement cybersecurity activities consistent with the CSMS. In practice, this requirement is discharged through contract clauses and supplier questionnaires. Whether the Tier 2 supplier manufacturing the Bluetooth stack has actually implemented the cybersecurity requirements passed down from the Tier 1 is a question most OEM programs cannot answer with evidence. The contractual obligation exists. The verification does not.
Third, the operational phase requirements — post-production vulnerability monitoring, cybersecurity incident response, and update management — are defined in the standard but are the least mature in practice. A vehicle certified under ISO/SAE 21434 at the point of type approval may have a credible CSMS for the development phase. The same standard requires that CSMS to function across the vehicle''s operational life, which for passenger vehicles can exceed fifteen years. The monitoring, triage, and OTA update integrity requirements for a fifteen-year operational window are in the standard. They are rarely in the program.
Example
An OEM with a mature ISO/SAE 21434 program — certified CSMS, complete TARA documentation for all in-scope items, supplier agreements updated — had a post-production vulnerability monitoring process that consisted of subscribing to NVD and three automotive-specific threat intelligence feeds. When a researcher published a new attack technique against a cellular modem chipset present in vehicles already in the field, the OEM''s process identified the relevant CVE fourteen days after publication. The gap analysis question was not whether they found it — they did. The question was what happened next: triage against specific affected vehicle configurations, impact assessment against the original TARA damage scenarios, decision on OTA remediation versus dealer update versus risk acceptance. That process took eleven weeks from CVE identification to remediation decision. The standard requires a cybersecurity incident response process. It does not define what ''timely'' means for operational vulnerability response in fielded vehicles.
ISO/SAE 21434 interfaces with several adjacent standards that organizations frequently treat as separate tracks: ISO 26262 (functional safety, ASIL), AUTOSAR security modules, and for software update management, ISO 24089. The interaction between functional safety requirements and cybersecurity requirements is explicitly addressed in 21434 but is underimplemented in practice — a cybersecurity control that degrades functional safety properties, or a safety mechanism that creates a cybersecurity attack surface, requires joint analysis that most organizations'' siloed safety and security teams do not perform.
What assessments of connected vehicle environments show
Assessment base: Vulnox connected vehicle and automotive supply chain assessments, 2023-2024
TARA attack feasibility miscalibration is consistent and directional
In technical assessments of components with completed TARAs, attack feasibility ratings assigned during the TARA process were lower than what hands-on testing demonstrated in the majority of cases involving network-accessible interfaces. Components assessed as requiring ''specialist expertise'' to attack were accessible to techniques documented in public automotive security research. The miscalibration was not random — it consistently underestimated feasibility for network-based attack paths and was more accurate for physical access scenarios. Engineering teams are more comfortable estimating physical access constraints than remote exploitation difficulty.
When attack feasibility is underestimated, risk values are lower than they should be. Cybersecurity goals derived from those risk values are less stringent than the actual exposure warrants. The TARA is internally consistent — the math is correct given the inputs. The inputs are wrong in a way that produces systematically insufficient cybersecurity goals for remotely accessible components.
Supplier CSMS implementations are nominal at Tier 2 and below
In supply chain assessments covering OEM-to-Tier-1 and Tier-1-to-Tier-2 relationships, Tier 1 suppliers with OEM contractual cybersecurity requirements had documented CSMS implementations in the majority of cases. Tier 2 suppliers — the component manufacturers whose software and hardware constitutes the actual attack surface of many ECUs — had cybersecurity programs that ranged from partial to absent. The contractual obligation to flow cybersecurity requirements down the supply chain existed in Tier 1 agreements. Evidence that the requirement had been flowed down and verified was present in a minority of assessed relationships.
An OEM''s ISO/SAE 21434 CSMS is only as strong as its weakest supplier''s implementation. For a connected vehicle with dozens of ECUs from multiple Tier 1 suppliers, each of whom sources components from multiple Tier 2 suppliers, the practical attack surface is shaped by organizations whose cybersecurity maturity the OEM cannot directly verify and whose TARA inputs the OEM did not validate.
OTA update integrity is documented but not adversarially tested
Organizations with over-the-air update capabilities had documented integrity verification mechanisms — code signing, secure boot, rollback protection. In assessments where we examined the OTA update pipeline end-to-end rather than reviewing the design documentation, the implementation gaps were at the boundary between the backend update server and the vehicle: authentication of the update server to the vehicle (not just the update package), handling of interrupted update sequences, and behavior under degraded connectivity. None of these were novel attack surfaces. All had been documented in automotive security research. None had been included in the TARA attack path analysis for the OTA subsystem.
A correctly signed update package delivered over a compromised channel, or a correctly signed package that can be interrupted mid-installation to leave the vehicle in a degraded state, represents a risk that code signing alone does not address. The TARA had assessed the update integrity controls and rated the residual risk as acceptable. The assessment had not included the channel and process integrity scenarios.
Safety-security interaction analysis is treated as a separate workstream
In every assessed OEM program, the ISO 26262 safety team and the ISO/SAE 21434 cybersecurity team operated with separate processes, separate documentation, and separate review cycles. Joint analysis of safety-security interactions — explicitly required by 21434 Section 15 — was documented as a meeting or a review step, not as an integrated analysis process. The practical consequence appeared in specific findings: cybersecurity controls that introduced latency into safety-critical communication paths, and safety redundancy mechanisms that created additional network interfaces with no corresponding TARA coverage.
A vehicle that satisfies both ISO 26262 ASIL requirements and ISO/SAE 21434 cybersecurity requirements independently may still have safety-security interaction risks that neither standard''s independent implementation catches. The interaction analysis is where the two standards'' requirements are jointly meaningful — and it is the least mature aspect of every assessed program.
The absence of prescribed controls makes ISO/SAE 21434 harder to implement well, not easier
Common belief
ISO/SAE 21434 gives organizations flexibility by not prescribing specific technical controls. This is an advantage over more prescriptive standards — organizations can choose the right controls for their specific architecture rather than implementing a fixed set that may not fit.
What we found
When we introduce findings from technical testing into an organization''s TARA review — presenting demonstrated attack paths that were not in the TARA''s analysis — the most common response is not to revise the TARA''s feasibility ratings. It is to add the specific demonstrated finding as a new threat scenario while leaving the underlying feasibility methodology unchanged. The finding gets addressed. The methodology that missed it does not.
The flexibility argument is correct in theory. In practice, the absence of prescribed controls removes the external reference point that engineering teams use to calibrate what ''sufficient'' looks like. When a standard says ''implement encryption for external interfaces,'' an organization knows what it needs to do and can verify it. When a standard says ''implement cybersecurity controls appropriate to the risk level derived from the TARA,'' the question of what controls are appropriate depends entirely on the quality of the TARA — and the TARA quality depends on the attack feasibility calibration, which is where we already know the systematic error is.
The result is that organizations have wide latitude to define their own standard of sufficiency, and that standard is shaped by what their engineering teams know how to build and what their program managers are willing to fund. The flexibility that was supposed to allow optimal control selection in practice allows organizations to build a coherent internal argument for whatever level of security they were going to implement anyway. The TARA provides the justification. The TARA inputs are not independently verified.
This is not a failure of the standard — prescribing specific controls for an industry with the architectural diversity of automotive would produce a checklist that was simultaneously over-constraining for some implementations and insufficient for others. But the implication for organizations is that the rigor of an ISO/SAE 21434 program is almost entirely a function of the intellectual honesty of the TARA process, and intellectual honesty in risk assessment is not something a management system standard can mandate.
Where ISO/SAE 21434 programs consistently fail to look
The fifteen-year operational tail
Passenger vehicles remain in service for an average of twelve to fifteen years in European and North American markets. ISO/SAE 21434 requires cybersecurity monitoring and incident response across the full operational life. The cybersecurity threat landscape in 2039 is not predictable from 2024. Most automotive cybersecurity programs have incident response and vulnerability management processes designed for the development phase and the first few years of production. The organizational commitment to maintain a CSMS, fund OTA update development, and respond to vulnerability disclosures for a vehicle platform fifteen years into its operational life is almost never addressed in program planning, because the people building the program today will not be accountable for it in 2039.
Third-party software components with no TARA coverage
Modern vehicle software stacks include significant volumes of open-source components, commercial middleware, and third-party libraries. ISO/SAE 21434 requires that cybersecurity activities address all components, including those sourced externally. In practice, TARA coverage of third-party software components is frequently limited to the interface between the component and the rest of the system, rather than the internal attack surface of the component itself. When a vulnerability is published for an open-source library embedded in a vehicle''s infotainment system, the TARA typically has no entry for that component at the level needed to assess impact quickly.
V2X and infrastructure-side attack surfaces
Vehicle-to-everything communication introduces attack surfaces that originate outside the vehicle. A compromised roadside unit broadcasting malicious V2X messages represents a threat that the vehicle''s TARA must address — but the attack surface is on infrastructure the OEM does not control and cannot harden. Most V2X security analysis focuses on the cryptographic integrity of the communication protocol. The scenarios involving persistent, low-and-slow manipulation of vehicle behavior through technically valid but adversarially crafted V2X data are less commonly in TARA scope, because they require threat modeling expertise in both automotive systems and infrastructure attack techniques simultaneously.
End-of-life cybersecurity obligations
ISO/SAE 21434 explicitly addresses decommissioning, requiring that cybersecurity considerations be applied when a vehicle or component reaches end of life. In practice, no assessed program had a documented process for managing the cybersecurity implications of end-of-life vehicles: persistent credentials stored in ECUs that could be extracted from salvage vehicles, connectivity services that remain active for vehicles no longer in manufacturer support, or the data residency implications of personal data stored in vehicle systems that pass through multiple owners before final disposal. The decommissioning clause is in the standard. It is not in the program.
Where this is heading
Within 36 months, a publicized exploitation of a fielded connected vehicle will trace directly to a Tier 2 or Tier 3 supplier component whose cybersecurity obligations were contractually flowed down from the OEM but never independently verified — and the regulatory response will force OEMs to demonstrate active supplier CSMS verification, not contractual attestation.
The supply chain verification gap is structurally consistent across every assessed OEM program. The contractual framework is in place. The verification capability is not. UNECE R155 holds OEMs accountable for their supply chain but does not currently specify the evidence standard for that accountability. A significant incident with a clear supply chain attribution will force regulators to define that standard explicitly. The precedent from other sectors — medical device supply chain requirements under EU MDR, software supply chain requirements emerging from US executive orders — points toward active verification requirements rather than contractual attestation.
Confidence: highIf no publicized automotive cybersecurity incident with confirmed Tier 2-or-below supply chain attribution occurs before Q4 2027, or if no resulting regulatory guidance requires active supplier CSMS verification beyond contractual attestation, this prediction is falsified.A new failure class will emerge — not yet named in automotive cybersecurity literature — where vehicles receive technically valid, cryptographically authenticated OTA updates that introduce cybersecurity regressions because the update validation process checks integrity and authenticity but not whether the update reintroduces a previously patched vulnerability or disables a previously implemented cybersecurity control. Call it authenticated regression.
OTA update security in automotive is currently focused on the integrity and authenticity of the update package. The question of whether an authenticated update is cybersecurity-safe — whether it maintains or improves the vehicle''s cybersecurity posture relative to the previous version — is not a widely implemented validation step. As OTA update pipelines become more complex and update cadences increase, the probability that a valid update introduces a regression grows. The TARA for the update subsystem assesses the integrity of the update mechanism. It does not assess the cybersecurity content of what gets updated.
Confidence: mediumIf by 2027 major OEM OTA update validation processes widely include cybersecurity regression testing as a mandatory gate, the structural condition for this failure class will have been addressed before it produces significant incidents.
The argument the industry is not having: should TARA validation be independently verified?
There is a question the automotive cybersecurity community treats as settled but is not: whether the TARA, as the foundation of every cybersecurity decision in an ISO/SAE 21434 program, should be subject to independent technical validation before it drives design decisions. The current practice is that TARAs are reviewed internally, sometimes by a second team, and checked by type approval auditors for process conformance. No one is checking whether the attack feasibility ratings reflect what an attacker can actually do.
My position is that mandatory independent technical validation of TARA attack feasibility ratings — not the whole TARA, specifically the feasibility calibration for remotely accessible components — would do more for actual automotive cybersecurity than any other single change to the standard''s implementation practice. The feasibility miscalibration is directional and consistent. It produces systematically insufficient cybersecurity goals for the attack surfaces that matter most. And it survives every internal review and audit cycle because everyone reviewing the TARA is using the same mental model of what ''specialist expertise'' means.
The counterargument is that independent TARA validation would add cost and time to development cycles that are already under pressure, that the automotive industry''s development timelines cannot absorb another mandatory external review step, and that the standard deliberately left technical specifics out to preserve flexibility. All of that is true. The cost and timeline argument would be more persuasive if the current approach were producing accurate risk assessments. It is not. The flexibility argument would be more persuasive if the flexibility were being used to implement stronger controls than a prescriptive standard would require. In assessed programs, it is being used to implement weaker ones.
Counterargument
Mandatory independent TARA validation would add 6 to 12 months to development timelines for major vehicle programs, create a bottleneck of qualified automotive security assessors that does not currently exist at scale, and reduce the flexibility that makes ISO/SAE 21434 applicable across the industry''s architectural diversity. The standard''s process requirements are sufficient if implemented with genuine rigor — the problem is implementation discipline, not the standard itself.
One thing to do this week
Pull the TARA for one externally accessible component — the telematics unit, the infotainment system, the OBD-II interface, whichever has the most network exposure. Find the three threat scenarios with the highest assigned attack feasibility. Now ask one question for each: what is the basis for the feasibility rating, and when was that basis last validated against what an attacker with current tools and published research could actually do? If the feasibility rating was set during the initial TARA workshop and has not been reviewed since, you have a risk value that may not reflect current reality. You do not need a full reassessment to answer this. You need someone with genuine offensive security knowledge to spend a day reviewing the feasibility inputs against current automotive security research. That review will either confirm the rating or surface the gap. Either outcome is more useful than the rating you have now.
Further Reading
phishing email analyzer
Phishing email analyzer: what real detection looks like in 2026password strength calculator
Password strength calculator: what the score actually measures and what it missesIoT device digital footprint small business
Your live camera is already indexed: IoT devices and your digital footprintISO framework group: ISO 27001, 27002, 27017, 27018, 27701, 22301, 31000, 42001 and more
ISO/SAE 21434 automotive cybersecurity requirements
Frequently Asked Questions
What does ISO/SAE 21434 require for automotive cybersecurity?
ISO/SAE 21434:2021 requires a Cybersecurity Management System covering the full vehicle lifecycle from concept through decommissioning. Its core technical requirement is a Threat Analysis and Risk Assessment for all items and components in scope. The TARA drives cybersecurity goals, which drive design requirements. The standard also requires post-production vulnerability monitoring, cybersecurity incident response capability, and OTA update management where applicable. It does not prescribe specific technical controls — cybersecurity requirements are derived from TARA risk values, giving organizations flexibility in control selection but placing significant weight on TARA quality.
What is the relationship between ISO/SAE 21434 and UNECE WP.29 R155?
UNECE Regulation 155 made a Cybersecurity Management System a type approval requirement for new vehicle types in the EU, Japan, and Korea from July 2022, and for all new vehicles from July 2024. ISO/SAE 21434 is the recognized standard for implementing the CSMS that R155 requires. Compliance with R155 requires demonstrating a conforming CSMS to a United Nations type approval authority — ISO/SAE 21434 certification or conformance is the primary mechanism for doing so. R155 holds OEMs accountable for their supply chain''s cybersecurity practices, extending the standard''s requirements beyond the OEM to its suppliers.
What is a TARA in ISO/SAE 21434?
TARA stands for Threat Analysis and Risk Assessment — the central technical methodology in ISO/SAE 21434. It requires organizations to identify damage scenarios (harm that could result from a cybersecurity attack), threat scenarios (how an attacker could cause that harm), and attack paths (the technical sequence). Each threat scenario receives a risk value based on impact severity and attack feasibility. Cybersecurity goals are then derived from risk values above a defined threshold. The TARA quality depends heavily on how accurately attack feasibility is calibrated — in practice, feasibility is systematically underestimated for network-accessible components.
How does ISO/SAE 21434 handle supplier cybersecurity obligations?
ISO/SAE 21434 requires OEMs to ensure that suppliers implement cybersecurity activities consistent with the OEM''s CSMS. This is typically discharged through contractual requirements and supplier questionnaires. The standard does not prescribe how OEMs verify supplier compliance — it requires the obligation to be flowed down, not that the result be independently validated. In practice, Tier 1 suppliers with direct OEM relationships have documented CSMS implementations in most cases; Tier 2 and below suppliers are significantly less mature. The contractual obligation exists at each tier boundary. The verification does not.
What is the difference between ISO 26262 and ISO/SAE 21434?
ISO 26262 addresses functional safety — the risk of harm caused by malfunctioning electrical and electronic systems, defined through Automotive Safety Integrity Levels. ISO/SAE 21434 addresses cybersecurity — the risk of harm caused by intentional attacks on vehicle systems. The two standards intersect where a cybersecurity attack could cause a functional safety failure, or where a safety mechanism creates a cybersecurity attack surface. ISO/SAE 21434 Section 15 requires joint analysis of these safety-security interactions. In practice, most organizations run the two programs separately with limited integration, which is where safety-security interaction risks accumulate.
Does ISO/SAE 21434 require post-production cybersecurity monitoring?
Yes. The standard explicitly covers the operational phase, requiring organizations to monitor for cybersecurity vulnerabilities and incidents in fielded vehicles, triage reported vulnerabilities against the original TARA damage scenarios, and maintain an incident response capability for post-production issues. Where OTA update capability exists, update integrity and process security are also in scope. In assessed programs, post-production monitoring is the least mature phase — most programs have vulnerability monitoring processes, but the triage-to-remediation decision cycle for fielded vehicles is poorly defined and slow relative to the exposure window a published vulnerability creates.
What are the most common ISO/SAE 21434 implementation gaps?
In Vulnox assessments, four gaps appear consistently: TARA attack feasibility ratings that underestimate remote exploitation difficulty, producing insufficient cybersecurity goals for network-accessible components; supplier CSMS implementations that are nominal at Tier 2 and absent at Tier 3; OTA update pipeline security that addresses package integrity but not channel integrity or regression scenarios; and safety-security interaction analysis that is documented as a review step rather than an integrated analytical process. The TARA feasibility gap is the root cause of the largest number of downstream issues.
Related Articles
Password strength calculator: what the score actually measures and what it misses
Password strength calculators measure entropy and character patterns. They do not measure whether a password has already been compromised. In Vulnox assessments, over 40% of passwords that scored "strong" on standard calculators appeared in public breach datasets.
Your live camera is already indexed: IoT devices and your digital footprint
An ESP32 cam streaming plant growth live sounds harmless. Shodan indexed it inside 48 hours. Here is what that exposes — and what a real attacker does next.
Phishing email analyzer: what real detection looks like in 2026
Most phishing email analyzers flag what attackers stopped using two years ago. In our assessments, 61% of phishing emails that bypassed automated filters shared one structural pattern — and it had nothing to do with links or attachments.
Ready to Secure Your Digital Assets?
Get a comprehensive vulnerability assessment for your website today.